Welcome to our News page dedicated to Information Security Services. Stay up to date with the latest news, trends, and advancements in the field of information security services. Our team of experts curates and delivers relevant news articles, insights, and analysis to keep you informed about the evolving landscape of information security services. Whether you’re an individual interested in personal data protection or an organization seeking robust cybersecurity solutions, this page is your trusted resource for staying informed about the latest developments in information security services.
Blog Topic: Exploring the World of Information Security Services: Protecting Data in the Digital Age
In today’s interconnected world, the protection of sensitive data has become a critical priority for individuals and organizations alike. Our comprehensive blog post explores the diverse landscape of information security services, providing valuable insights into the range of solutions available to safeguard data in the digital age. From managed security services to penetration testing, incident response, and beyond, we delve into the key offerings and benefits of information security services. Whether you’re a business owner, an IT professional, or simply someone concerned about protecting your personal information, this guide equips you with a deeper understanding of the services available to mitigate risks and fortify your digital defenses. Stay informed and empowered with our expert analysis and practical recommendations on information security services.
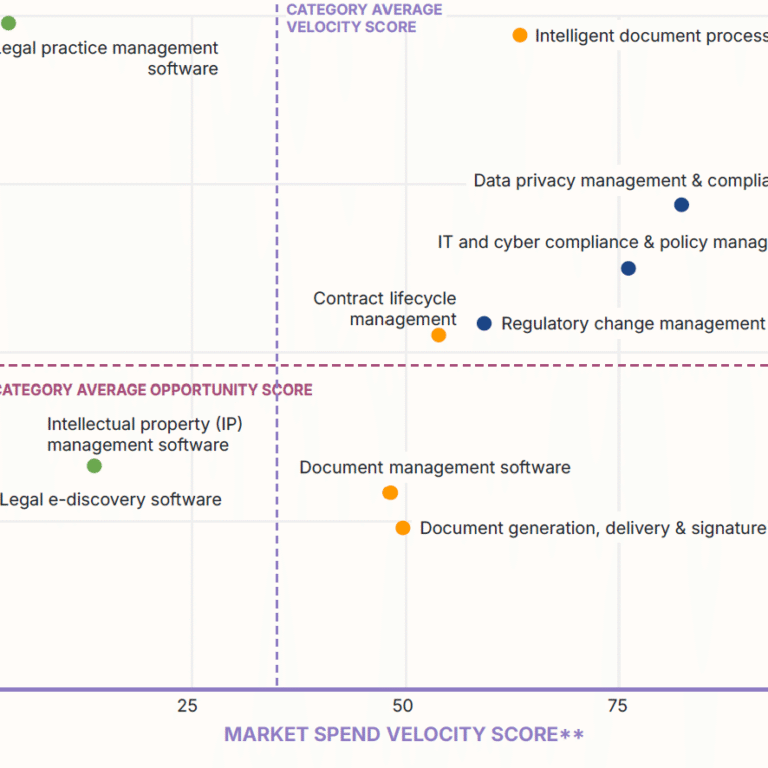
In 2025, the Legal and Document Tech market is shaped by three main forces: the growing complexity of regulations, the maturity of AI-driven tools, and increasing pressure on operational efficiency. Based on the Qualitate report “The State of Legal and Document Tech: The Winning Playbook for 2025”, we highlight key technical trends for legal…
1️⃣ Ransomware ≠ Encryption Traditional encryption is no longer the primary monetization method. The main business model has shifted to data theft and extortion-first. Leading actors: RansomHub, Akira, INC/Lynx. The focus is on stealing sensitive data and applying pressure through potential leaks and publications. 2️⃣ RAT + RMM as Standard Access Vectors 75% of remote…
The transition from PCI DSS 3.2.1 to version 4.0 marks one of the most significant updates in the payment security landscape. While the technical controls get much attention, one key area remains underestimated: regulatory documentation. For companies handling cardholder data — especially in fintech, crypto, gambling and e-commerce sectors — this documentation is not just…
As artificial intelligence becomes an integral part of modern infrastructure, its implementation brings not only new opportunities but also a wide spectrum of cyber risks. The document “Critical AI Security Guidelines” offers a structured approach to understanding these risks and applying practical security measures. This article summarizes the core principles and actions necessary to establish…
The development of artificial intelligence (AI) is significantly impacting information security compliance requirements. Companies and regulators are already facing new challenges related to automated threats, data protection, and ethical standards compliance. 1. New Data Protection Requirements AI increases the volume of processed data, necessitating stricter control over its storage, processing, and transmission. Heightened privacy concerns:…
Analysis of Global Cybersecurity Trends: Global Cybersecurity Outlook 2025 Introduction The modern cyber landscape is becoming increasingly complex, with digital risks growing more sophisticated. The “Global Cybersecurity Outlook 2025” report, prepared by the World Economic Forum (WEF) in collaboration with Accenture, analyzes key challenges facing organizations and proposes strategies to enhance cyber resilience. Key Challenges…
Introduction The year 2024 has become a turning point in the development of artificial intelligence (AI). While technologies continue to evolve rapidly, the industry faces new challenges and opportunities. The report ‘2024 Backward Pass – The Definitive Guide to AI in 2024,’ prepared by Kelvin Mu from Translink Capital, provides an in-depth analysis of key…
The Digital Operational Resilience Act (DORA) will significantly change the way financial institutions manage their data security. DORA requires all financial institutions to implement a cybersecurity program that includes policies, procedures, and risk management activities. These policies must be reviewed annually by a third-party financial regulator, who will assess their adequacy based on industry standards.…
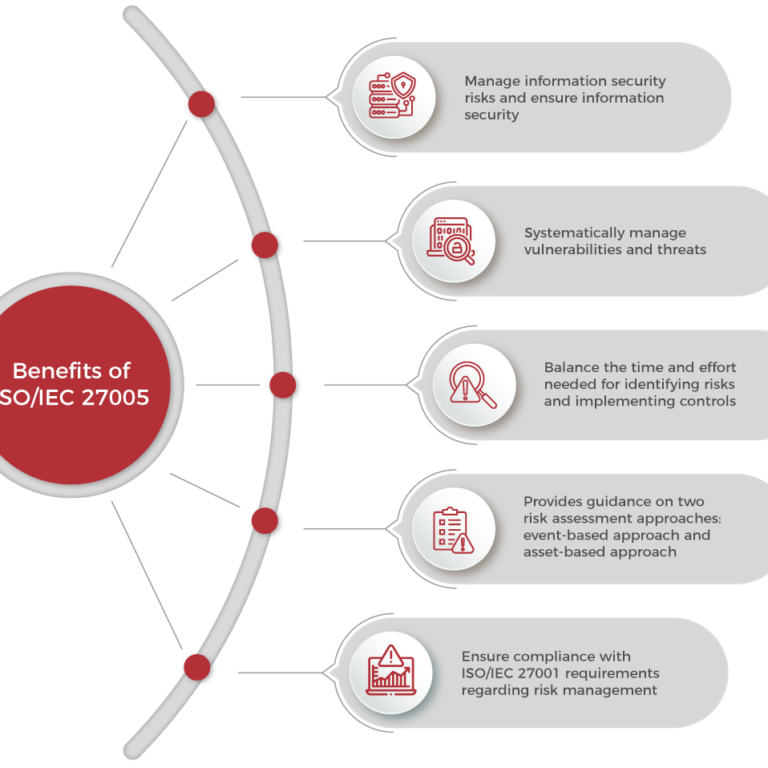
27005 – 2022 Information security, cybersecurity and privacy protection — Guidance on managing information security risks ISO/IEC 27005:2022 provides guidelines for information security risk management. Knowledge of the concepts, models, processes, and terminologies described in ISO 27001 and ISO 27002 is important for a complete understanding of this standard. This document supports the main concepts…